Passkeys Explained: Why Every App Is Suddenly Asking You to Set One Up


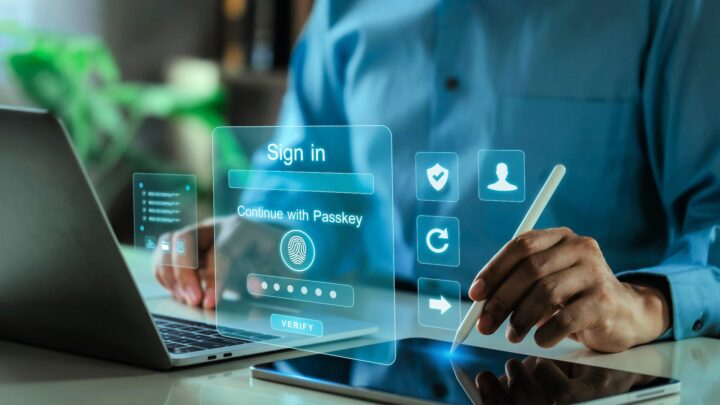
If you’ve noticed almost every app and website you use lately nudging you to “create a passkey,” you’re not imagining it, and you’re certainly not alone in wondering what exactly you’re being asked to sign up for. Here’s a plain-English explanation of what passkeys actually are, how they work, and the genuine issues worth knowing about before you dive in.
What is a passkey?
A passkey is a way of logging in without typing a password at all. Instead of a word or phrase you need to remember, your phone, tablet or computer stores a unique digital key, and you simply unlock it the same way you already unlock your device: with your fingerprint, your face, or your PIN.
Technically, passkeys are built on something called FIDO2 and WebAuthn, open security standards backed by Apple, Google, Microsoft and the broader tech industry. When you set one up, your device creates two matching digital keys. One, the private key, stays securely on your device and never leaves it. The other, the public key, is given to the website or app. When you log in, the website sends a little digital puzzle, your device solves it using the private key, and the site checks the answer against the public key it already has. Nobody ever types, sends or stores an actual password in this process.
How is it actually different from a password?
The simplest way to think about it: a password is a secret you remember and can accidentally give away. A passkey is a secret your device holds and never actually hands over to anyone, including you.
This matters because it directly closes off two of the biggest ways people get hacked. Firstly, passkeys can’t be phished. Since a passkey is cryptographically tied to the genuine website it was created for, a fake lookalike site simply can’t trick your device into handing over a usable credential, the way a convincing fake email can trick you into typing in your real password. Secondly, passkeys can’t be stolen in a data breach. When a company’s database gets hacked, there’s no password sitting in a file for criminals to steal, because your actual key was never stored on their system in the first place, only the public half, which is useless to a criminal on its own.
The genuine issues worth knowing about
Passkeys are a real, meaningful security improvement, but they’re not entirely without their complications, and it’s worth going in with your eyes open.
Losing your device is the biggest risk. If your passkeys are “synced,” backed up through iCloud Keychain on Apple devices, Google Password Manager on Android, or a password manager like 1Password or Bitwarden, they’ll automatically restore when you sign into a new device. But if a passkey is “device-bound,” meaning it only ever lived on that one phone or laptop, losing that device without a backup can mean genuine trouble getting back into your account.
Account recovery remains the weak point. If you ever do lose every device holding your passkeys, with no backup in place, you’ll generally fall back on the same recovery process as before, usually a code or link sent to your email. This means your email account genuinely deserves your strongest possible protection, since it effectively becomes the master key to everything else if your passkeys are ever unavailable.
Not every website supports them yet. While major banks, email providers and tech platforms have widely adopted passkeys, plenty of smaller sites still rely on passwords only, so most of us will be juggling both systems for some time yet.
Moving between Apple and Google can be clumsy. If you use an iPhone but also a Windows laptop, or switch from Android to Apple down the track, passkeys don’t always transfer smoothly between different companies’ systems, which can be a genuine source of frustration.
The most important piece of advice
Given all this, the single most useful thing you can do is test your recovery process before you delete any of your existing passwords. Set up the passkey, sign out, then deliberately try signing back in on a second device to confirm it genuinely works and that you know how you’d get back in if your phone were ever lost or broken. Only once you’ve confirmed that should you consider removing the old password as a backup.
Should you bother setting them up?
For most people, yes, it’s genuinely worth it, particularly for your most important accounts: email, online banking, and anywhere storing sensitive personal information. Start there rather than trying to convert every single account you own at once. Given how often passwords get reused, written down, or fall for a convincing scam email, a passkey is a real, practical step toward making your most important accounts considerably harder for a scammer to break into.
This article is general in nature and isn’t personalised technical advice. If you’re unsure how to set up passkeys on your specific devices, your bank or service provider’s help centre, or a trusted family member, can usually walk you through it safely.


 Proudly Australian owned and operated
Comments 0
Join the conversation. Comments are reviewed before they appear.
Be the first to comment.
Join the conversation
Tell us who you are to post a comment. We'll remember you next time.